EU CRA System Integration: Connecting PLM, SBOM Tools and Polarion
Do companies have to replace their existing PLM or deploy an entirely new system to meet CRA cybersecurity requirements?
Not necessarily.
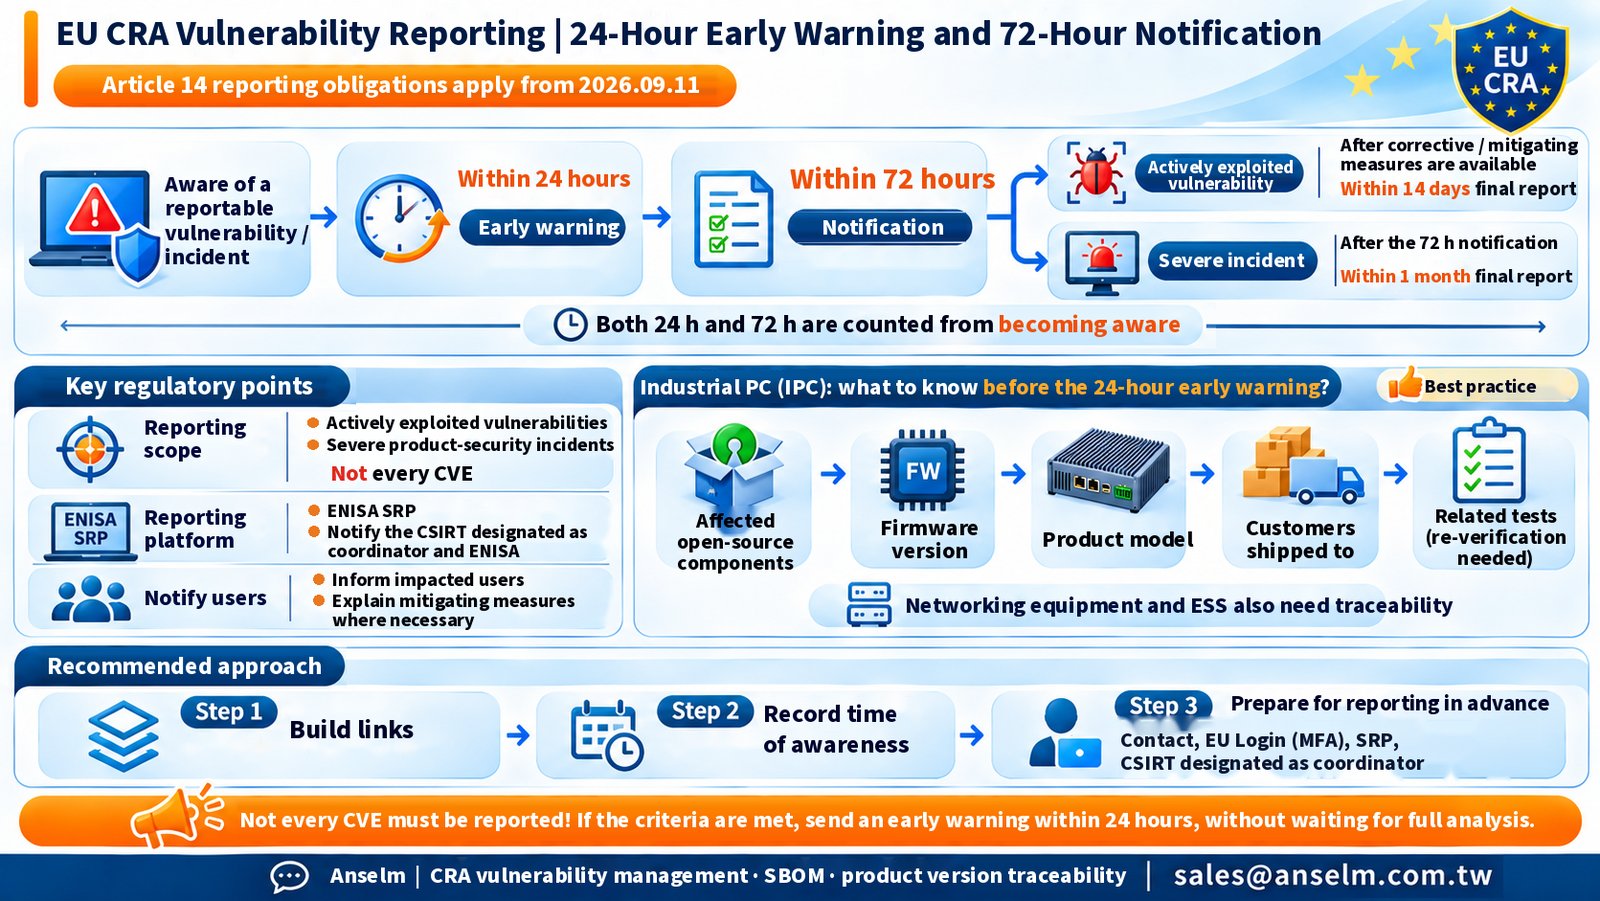
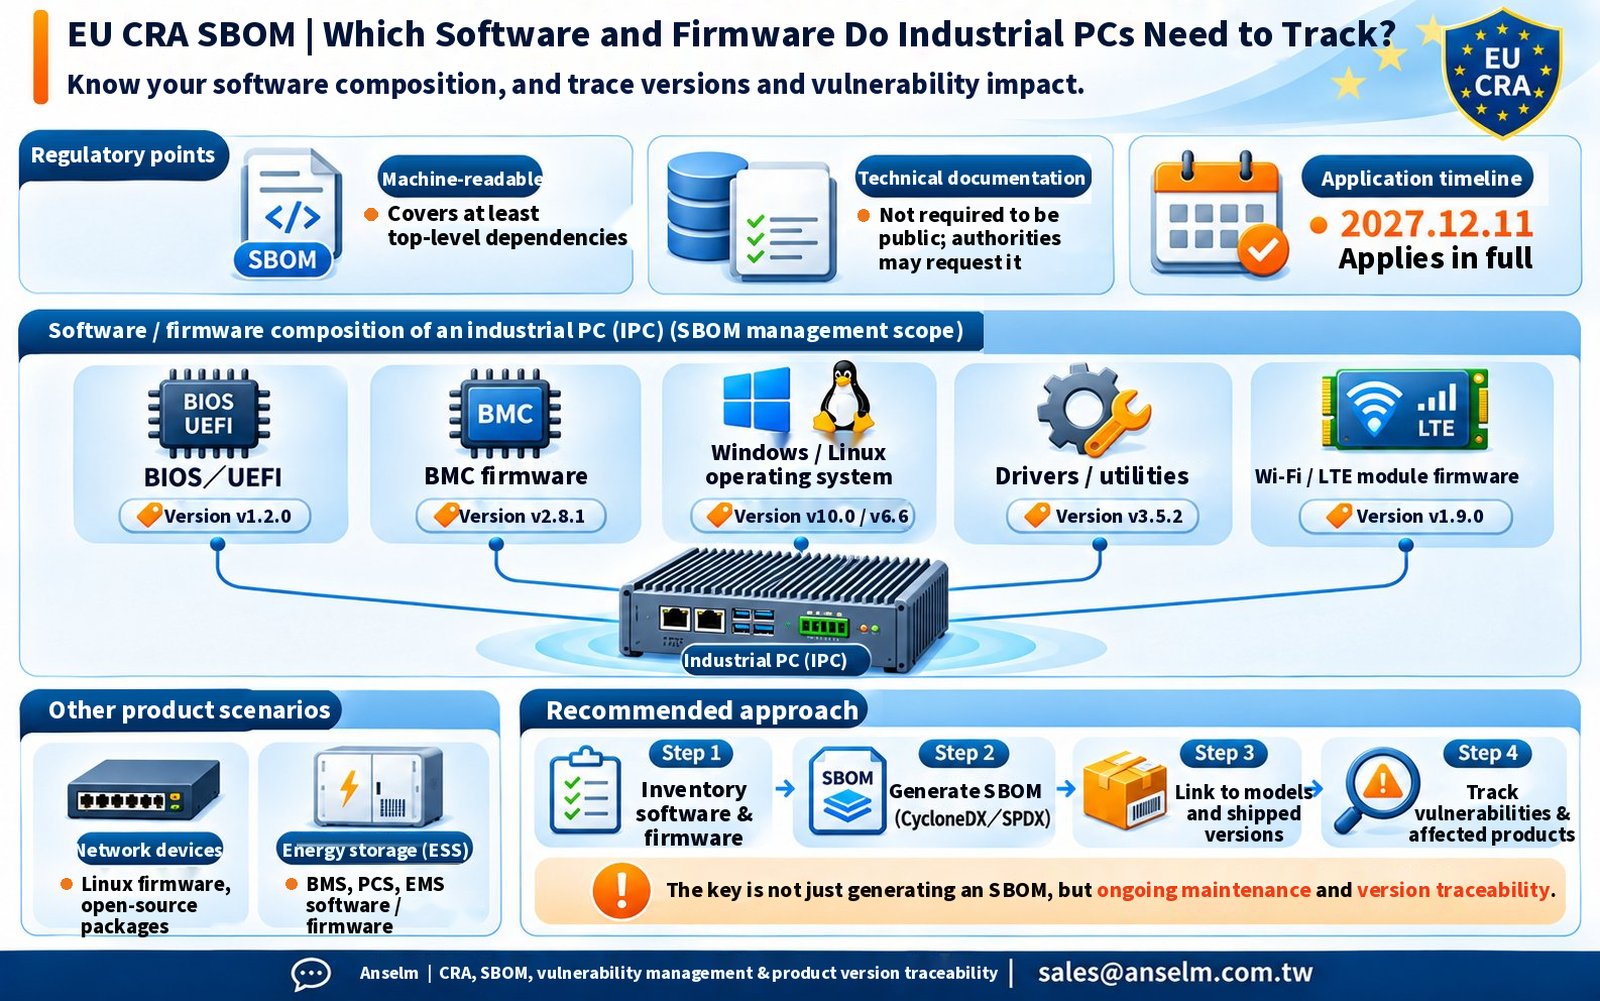
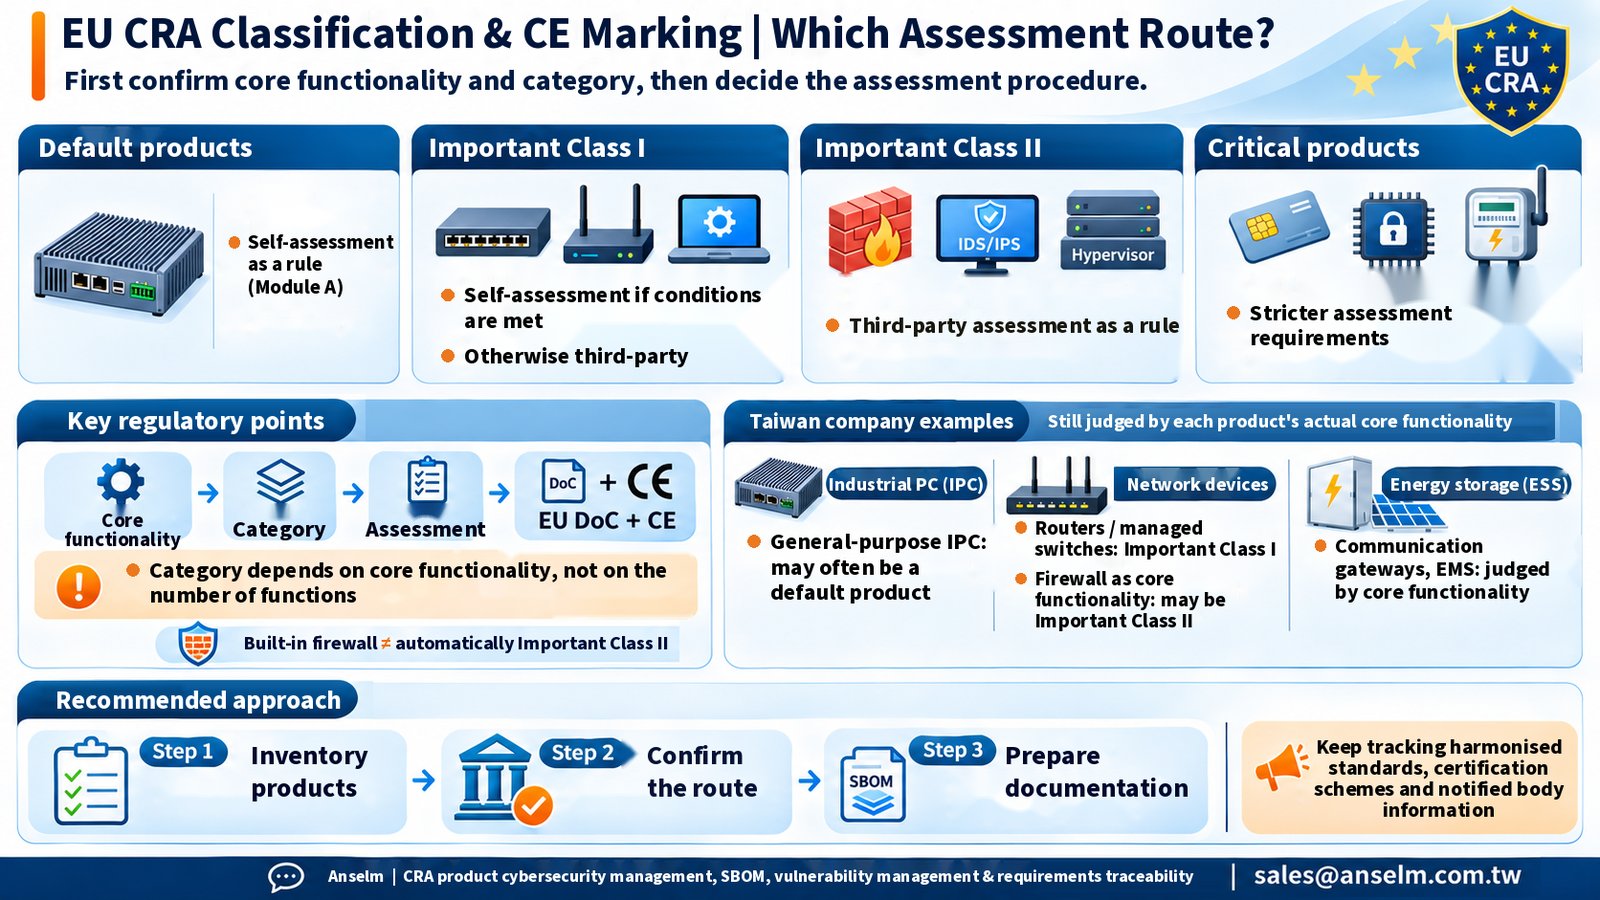
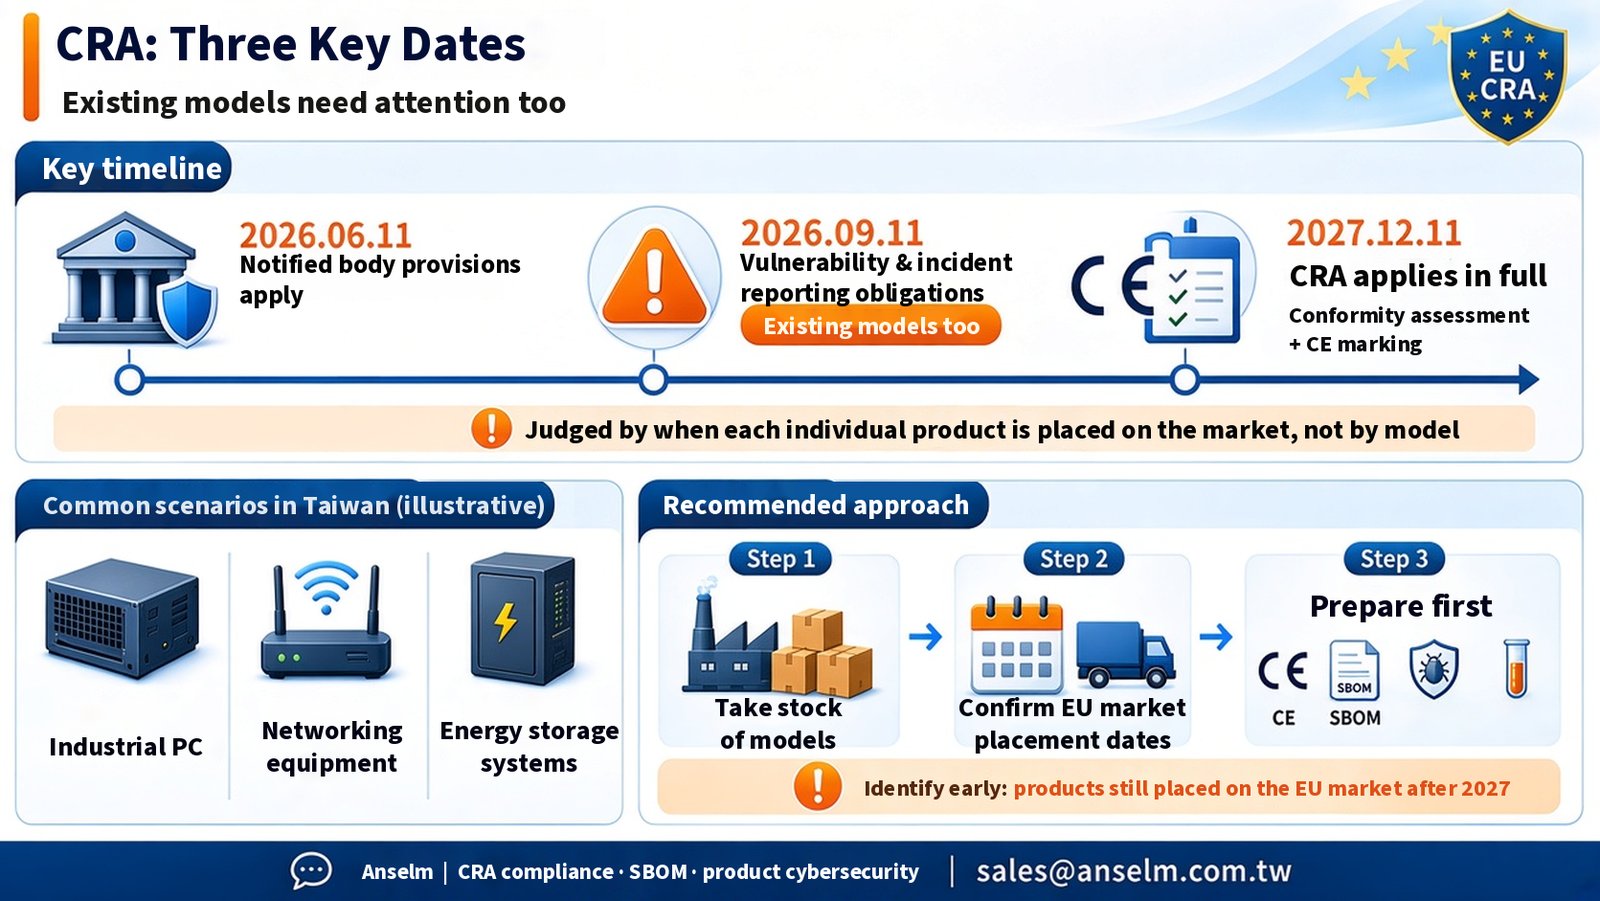
The EU Cyber Resilience Act (CRA) will apply in full from 11 December 2027. The reporting obligations under Article 14 have applied since 11 September 2026, and they also apply to products placed on the market before 11 December 2027.
The CRA does not prescribe any particular software. The real challenge is whether a company can link product information, security requirements, vulnerability handling and test records, and provide traceable, auditable technical documentation.
📌 Three key management priorities under the CRA
🔹 Tracing vulnerability impact: When a vulnerability is found in a software component, if the SBOM is already linked to product versions and the BOM, the affected firmware versions and product models can be narrowed down more quickly. If ERP/shipment data is also connected, it can further help identify the customers who received the affected shipments.
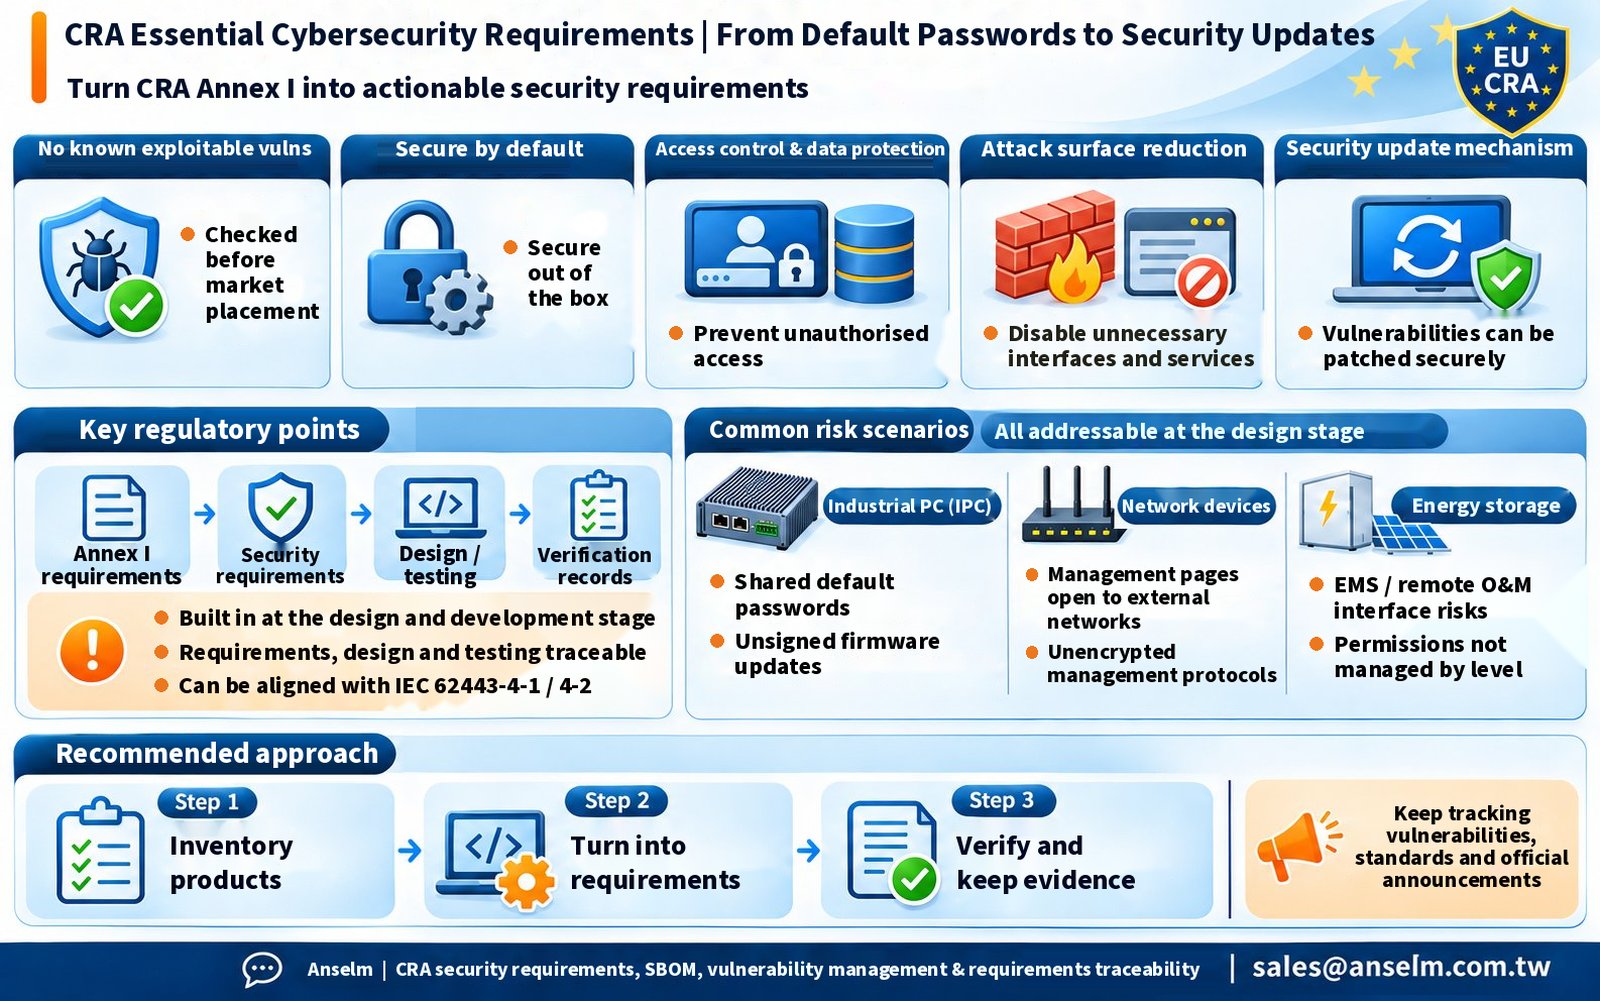
🔹 Auditable cybersecurity documentation: Link cybersecurity risk assessments, security requirements, test and verification records, and SBOMs to support the preparation of CRA technical documentation.
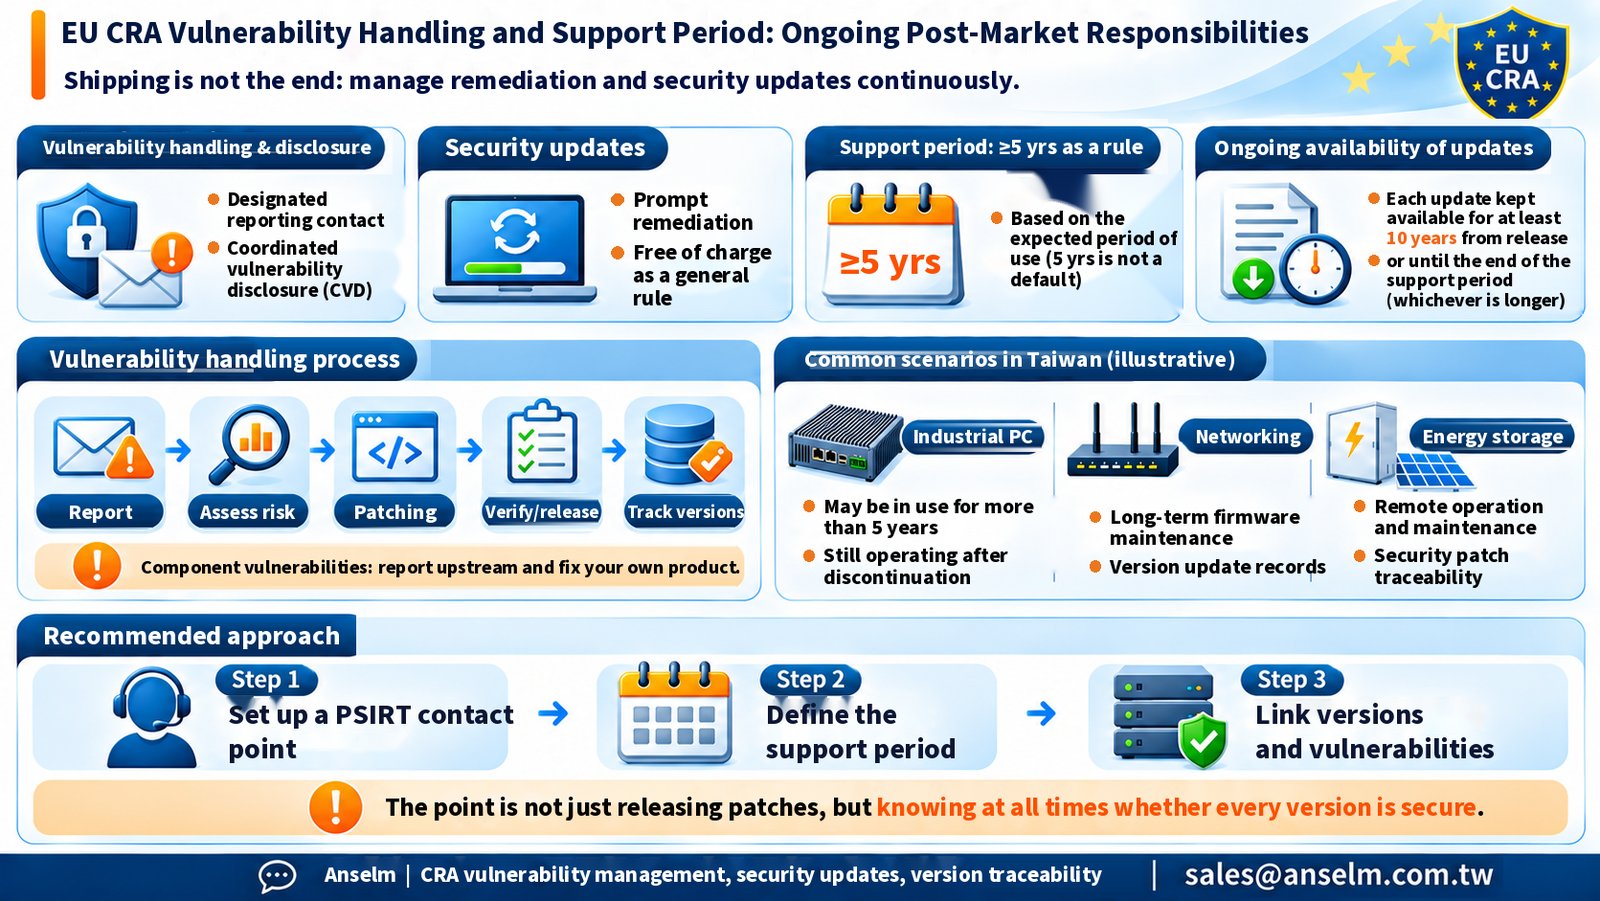
🔹 Ongoing post-market management: Throughout the support period, keep recording vulnerability handling, security updates and product version changes.
🔍 Is your company facing any of these challenges? (Illustrative common industry scenarios, not legal requirements)
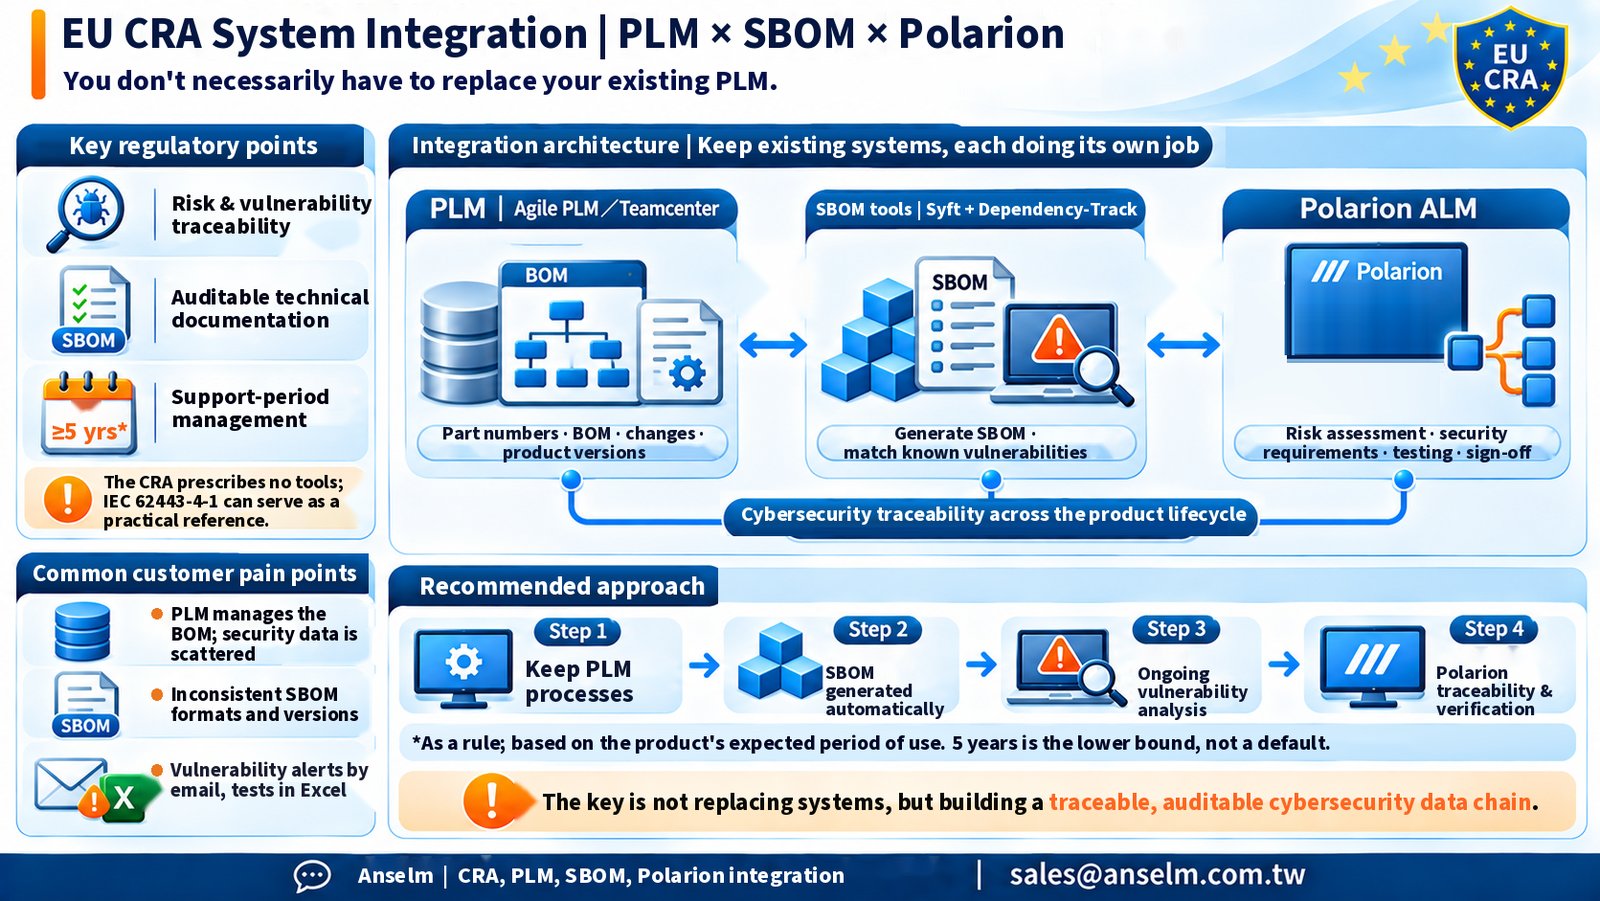
🔸 Part numbers, BOMs and engineering changes are managed in Agile PLM or Teamcenter.
🔸 SBOMs are produced by different R&D teams, with inconsistent versions and formats.
🔸 Vulnerability information is passed around by email, making assessment and remediation status hard to track.
🔸 Security requirements and test results are scattered across Excel files and other documents.
⚠️ When a vulnerability occurs, departments have to cross-check data manually to identify the affected products.
💡 How can you build a CRA traceability architecture on top of your existing systems?
We recommend letting three types of systems each play their own role:
🔹 PLM | Oracle Agile PLM / Siemens Teamcenter: Keep your existing processes for managing part numbers, BOMs, product versions and engineering changes.
🔹 SBOM tools | Syft + OWASP Dependency-Track: Generate SBOMs with Syft (output in CycloneDX format for import into Dependency-Track); Dependency-Track then continuously checks components against known vulnerability data sources to analyse software component risk.
🔹 ALM | Siemens Polarion: Manage cybersecurity risk assessments, security requirements, remediation tasks, test and verification, and electronic sign-off records (configured according to project templates and workflows) to establish a traceable management process. Anselm (安盛資訊) has developed an integration between Dependency-Track and Polarion, which can be combined with CI/CD pipelines to bring vulnerability analysis results into Polarion for assessment and tracking.
With appropriate system integration, companies can establish:
Product version ↔ SBOM components ↔ Vulnerability assessment ↔ Security requirements ↔ Test and verification
reducing the reliance of vulnerability handling on manual searches and scattered documents.
✅ Anselm has developed a data integration between Polarion and Oracle Agile PLM, so companies can go on to plan a CRA product cybersecurity traceability architecture while keeping their existing PLM management processes. The actual integration approach is planned according to each customer’s existing systems and data structures.
Companies can also refer to the IEC 62443-4-1 secure development lifecycle process to build, step by step, a cybersecurity management framework suited to their own products. IEC 62443-4-1 is not currently listed as a CRA harmonised standard.
⚠️ CRA compliance is not about how many systems you replace. It is about making the data across your systems linkable, traceable and auditable.
👉 Want to learn how to integrate your existing PLM, SBOM tools and Polarion to build product cybersecurity traceability?
Get in touch with Anselm.
📩 Contact Anselm: sales@anselm.com.tw
Further reading: Previous article: EU CRA Vulnerability Handling and Support Period: Ongoing Post-Market Responsibilities | This is the final article in the series: Back to the EU CRA series overview
This article is for general information only and does not constitute legal advice. Product capabilities are subject to each vendor's public documentation and the actual version and licence plan. Official sources: Regulation (EU) 2024/2847 (Recital 8; Articles 13(8), 14, 69(3) and 71(2); Annex VII); Siemens Polarion Cybersecurity; Polarion X 2512: What's New and Noteworthy; Siemens Polarion on CRA compliance; OWASP Dependency-Track file formats; Anchore Syft.